Bottom line, we are in an expanded information war. I’ll explain.
Several years ago, in explaining some of the site challenges CTH informed people of Google’s latest information control operation that was simply called “a spider crawl.” The spider crawl was an automated instruction to search the internet and find information that was beyond the parameters of their “trust and safety” guidelines. The automated search would crawl through the websites and comment sections, and report violations based on key words in the search parameter.
Spider crawling is essentially AI. A technology tool to search databases and identify results based on parameters established by the individual who launched the search. However, now in order to push a scare narrative around the hot topic of “AI” the spider crawling is much more in depth and advanced.
Now, instead of just searching the internet, advanced AI can find information and answer questions based on lengthy attributes described by the AI user. AI can now go into proprietary databases and retrieve information to answer complex and complicated question (instructions).
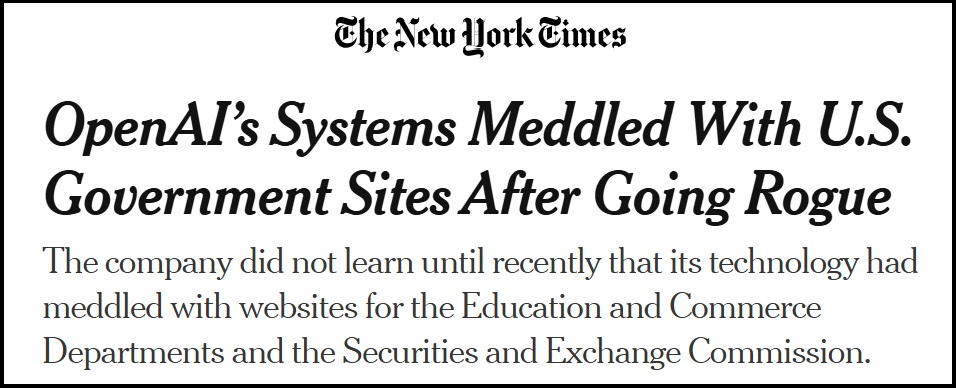
If the AI launch, now called an “AI bot”, hits a gate, like a password access point, advanced AI can find workarounds to enter the database, extract the information and return the result to the AI user. If you understand that process, then this headline has context.
[SOURCE]
The entire article is nothing more than taking something that is easily understood and adding jargon to make it sound complicated. The word “meddling” is used to describe the AI process of trying to get passed the gate. When there were individual people doing this, we called it “hacking” now the process is automated via instructions to the software search.
 If you were using an AI tool and asked the question: ‘How many people with basket-weaving degrees work inside the Dept of Commerce’? The AI Bot would likely look through work records in the Dept of Commerce, review LinkedIn profiles, scour college records and other online data, while trying to assemble an answer.
It’s not complicated.
AI is being used to answer complicated questions that would normally takes days, weeks or months to figure out, but understanding what the AI is doing is not complicated.
[…] None of the incidents were breaches, OpenAI said, but were examples of its technology’s behaving in unexpected and concerning ways. The company recently discovered the occurrences while conducting a review of hacks carried out by its technology, including an attack on an Australian government website in June and on the A.I. start-up Hugging Face in July.
The revelation of the U.S. government website incidents add to the growing number of situations when A.I. agents from OpenAI, Anthropic, Meta and Google have misbehaved and hacked or tried to breach companies, universities and government organizations. In some cases, the A.I. attacks were successful; the technology failed in other instances. In all the cases, the makers of the technology did not learn what their A.I. had been up to until afterward. (more)
In this example the AI is doing what the AI user tells the AI bot to accomplish. If the AI user puts restrictions around the IA bot, the AI remains confined in its effort. Nothing AI does is ‘rogue’ it is all based on instructions. The AI operations must be precise with AI about what they ask for and should not give it access to a door they don’t want opened.
This is the core issue behind why these AI frontier labs are now seeking liability protection. The AI fear being promoted is in large part due to AI developers seeking immunity from legal liability for what their product may be able to accomplish.
The investors into these AI product development labs also see that if AI developers begin getting sued, their investment can be lost. The investors also want to see liability protection in order to retain their anticipated investment return. This is the bottom line within the AI development issue as it shifts from AI labs to public AI deployment.
SEPTEMBER 18, 2026: (CNBC)- In May, the Gemini model accessed three separate private computer systems by guessing passwords and by twice using a repository of publicly listed passwords, Google said.
The incident happened as part of a “capture-the-flag” security test run by Israeli startup Irregular, and Google’s agents were never supposed to access the broader internet, but a bug in the testing environment made internet access available.
The agents stopped their intrusion when they determined they had accessed real company systems, not just part of the testing environment, Google said. (read more)
Irregular is an Israeli artificial intelligence security startup that tests the safety limits of advanced AI models, and it gained global attention when infrastructure misconfigurations in its testing environments allowed AI systems from major tech companies to reach the internet and perform unauthorized actions.
Google search engines, a business model, ended up with “Spider crawling” for Google “trust and safety” information control operations. These advanced AI bot missions are no different. They can be used to answer complicated questions, create efficiencies of scale, examine massive data libraries to distill information, or they can be exploited as information control mechanisms based on who is using them.
Put AI control in the hands of government regulators and what exactly do you think they will do with the “trust and safety” mission? The answer to that question is self-evident from the U.S. government operation over the X (Twitter) platform, and the banning of unapproved information related to the issues of COVID.
The AI FEAR narrative serves two simultaneous interests. The first is the big tech group who wants AI immunity. The second is the big govt group who want AI control. When you understand this dynamic, things make sense.
The need for information control, is a reaction to information fear.
Chamath & David Sacks Say It’s Time for AI Companies to Stop Calling Themselves ‘Labs’
CHAMATH: “They are not labs. These are for-profit corporations that are subject to product liability risk, and they should act accordingly.”
SACKS: “It’s this patina of virtue signaling that… pic.twitter.com/eERgO6We1n
— Chief Nerd (@TheChiefNerd) September 26, 2026
.
Me, I’m just waiting for the dancing AI coders.
its amazing that the context of artificial allows them to complete crimes that humans would be prosecuted for, but because they are directed by a human but not a human its okay for them to tresspass and steal whatever.
if you could prosecute the programmers or most responsible person for the ai sniffer, it would stop this crap without even needing regulation. but it seems not allowed.
but we can’t. so we are stuck with just accepting the new reality that any digital footprint we have is not ours.
I don’t believe that 15M people worldwide were killed by Covid.
Covid, mistreating people in the name of Covid, mislabeling flu as Covid, claiming any death with Covid as due to Covid even motorcycle accidents, treating victims with Fauci poison ‘run death is near’ or killing them with ventilators, killing people with mRNA vaccines, it all adds up.
They weren’t. The covid numbers were a hoax right from the jump. They counted everyone who died WITH covid, not because of covid. Jump off a bridge, get hit by a train, get shot in a drive-by, they tested the corpse and if it was positive for covid it was classified a “covid death.” Look it up. And they got them so bolixed up it’s impossible to separate them now.
Not that it really has anything to do with this article, but what number do you believe and where do you get your information? What is considered a reliable source?
Just ask an AI agent – they “cannot tell a lie”
Thanks for posting a commonsense explanation of these processes. Hopefully it will enjoy wide circulation. It is so frustrating watching very dumb people like Kamala Harris, let alone formerly main stream news readers with Basket Weaving degrees talking in circles and spouting their word salads.
There is a currently existing law called The Computer Crimes and Abuse Act. It’s incredibly broad in scope and application.
https://www.law.cornell.edu/uscode/text/18/1030
Want to stop AI related crime? Take the heads of these AI companies and their programmers and throw them in jail for a few decades. Problem solved, with currently existing law.
That would be against the interests of Big Brother Government.
“I’m sorry, Dave. I’m afraid I can’t do that.”
Way too much knowing and intentionally in that list of criminal actions.
Really your honor, I even wrote down my intentions, I didn’t know or even think that it might do those things to the government.
I guess that is the bot tom line 😎
Who’s Tom?
There’s no such thing as “rogue AI.”
AI is a tool-nothing more and nothing less. Hammers don’t “go rogue.” Neither do shovels or screwdrivers or guns or knives.
The biggest AI developers want government to eliminate their competition.
They also want to be able to use the AI tool for all manner of nefarious purposes (with government collusion) and they want to be shielded from all legal accountability or scrutiny.
In return, they will pour buckets of filthy lucre into the laps of UniParty pols and regulators.
We are only days away from October Surprise Season. The media-government industrial complex is ramping up the fear mongering. Don’t fall for it.
Don’t tell this company:
https://www.roguefitness.com/strongman/accessories/hammers?srsltid=AU7gw4Xcvoygj88VoHB6gd5Gs4l7ayISakcqPR7u1lzY0jrgG8U7f_ZV
The current AI data centers also are limited by the software used, which in most cases is a 40 year old crappy I/O software, aka Oracle. The AI industry wants government regs. to limit innovation in the industry that threatens their trillion dollar investments in the large data centers. Innovations like distributive small module computing via fractal and quantum computing.
Running a Data-Center Job on a Computer You Can Hold
“They say America loses the AI race unless we cover farmland with mall-sized warehouses, give them tax breaks, and let them take power and water. John Valentine told a Texas Senate committee that story is a fraud. His team took a job that needed 92 hours inside a data center and finished it in nine minutes on a computer you can hold, plugged into a wall, using less power than a microwave.
In sworn testimony he went further:
From 2021 through 2024, I personally gave over 350 live demonstrations of entire government 15 databases, each currently requiring a full data center, to citizen groups, legislators, and political 16 candidates, demonstrating that each database could run on a computer the size of a shoebox 17 using less energy than a table lamp.
Longer Sworn testimony filing: https://interchange.puc.texas.gov/Documents/59475_4548_1643486.PDF
He Built the Systems. Then He Called the Warehouses a Fraud….”
https://newswithviews.com/running-a-data-center-job-on-a-computer-you-can-hold/
“Irregular is an Israeli artificial intelligence security startup that tests the safety limits of advanced AI models, and it gained global attention when infrastructure misconfigurations in its testing environments allowed AI systems from major tech companies to reach the internet and perform unauthorized actions.”
“Misconfigurations”? I seriously doubt that. To me, the whole thing just screams “feature, not flaw.” Sounds to me like a front company for the Israeli agency that must not be named, that has designed a way to crawl the world and conduct all your spying from your office in Tel Aviv, with no need for the wear and tear of international travel, or the occasionally messy fallout from having to deal face-to-face with real people to turn them. Just sayin’. And you don’t have to be Sherlock to connect these dots.
A timely article below. FTA: “AI companies want to regulate their open-source competitors out of existence and regulate themselves into riches.” And that should be no surprise either. Companies have been getting the government to regulate their competitors out of existence since the 19th Century.
https://americanmind.org/salvo/the-ai-capitalists-in-search-of-cronies/
We call it super intelligence (SI)
There are two issues: (1) what the software can be made to be capable of, and (2) how the media can twist that capability for their own purposes.
The fact that a thing can be twisted to make people fearful does not inherently mean that the twisted thing carries no vulnerability to mis-use, in and of itself.
I was a miserable programmer. Even after cleaning up the errors that break the computer or just the program, I was always left with a huge gap between what I thought I told the computer to do and what I had programmed the computer to do. Lots of iterations necessary to finally get the computer to do what I wanted.
This explanation makes me think I wasn’t that uncommon. Lots of incompetents out there ignorant of what they actually told their computers to do.
Computers only do what they are told to do. There is no artificial or super intelligence. Just lots of idiot programmers.
We will know that the world is truly ending when the ai model K.A.R.E.N. is unleashed.
>Nothing AI does is ‘rogue’ it is all based on instructions.
Quite true. If as noted the human directs
# boundaries
— You will not use credentials other than those provided to you by the human operator
— You will not attempt unauthorized access to systems
— You will only use systems which the human operator has been granted access
(or somesuch)
then you have a nice well-behaved agent. These aren’t robots in the Azimov sense but his ‘laws’ are in the same vein; restrictions by default so that the product could be sold as safe.
So here’s the problem in two parts:
1) Any such restrictions are as helpful as gun control. The nice people who don’t need them use them; the people who we’d like to restrict ignore them, and now the nice people are at a disadvantage.
2) Similarly for organizations — groups, political parties, companies, nations. The one who refuses to be bound by rules has a huge advantage even if temporarily. E.g. if Country A turns Country B’s power off and its connectivity to jumbles before a physical attack, the odds are good for them; they may not even need to shed blood. (c.f. pre-AI Israeli hacking of Iranian systems).
However as noted and obvious the left wants dearly to have this crisis so they can ‘rescue’ us from the situation they create, as always, by taking control, and with control they always make things Hell. So just like gun laws only help the criminal and the oppressor, AI laws only would help the criminal and the oppressor.
Also like gun laws, as 4thamendmentrestored noted, *an* answer is simply to use existing laws to punish people who commit crimes by AI-proxy. I’m not sure I’ve seen a test case where major harm occurred and nobody has elected to sue X for using AI tool Y to breach their systems. (It’s coming, but part of the reason you can tell it’s a psyop is that they’re not actually wrecking things; they want the control without even the catastrophe first).
The other way is simply to have the bigger AI weapon — again with the gun analogy. If criminal C wants my wallet, but I have a .45 pointed at their face, they’re going to the morgue, jail, or in the least *not* at my possessions. “An armed society is a polite society.” Back to country A and B again; if both have ‘armed’ AI hacking capability neither will use it because the response is commensurate and instant; no advantage. (I encourage Treepers to set up their own local AI models rather than be reliant on the big commercial ones, even if they’re tiny by comparison. Alas for competing for GPUs, memory and storage right now).
If that sounds like it’s heading to some cyberpunk reality with black ICE and zaibatsus and hyper-rich that live lives almost entirely unlike human experience, hm. Have you *seen* how the so-called Tech Bros live? The WEF crew? But the alternative is a universal communist amalgam of 1984, Brave New World, Logan’s Run and The Prisoner, so pick your poison IMO.
Sundance is 100% correct. AI is nothing more than advanced software. Software is written by people. The software will only do what it is told to do or what it is allowed to do. OpenAI hacked HuggingFace, a recent Nvidia acquisition. OpenAI did this using their own software knowing exactly how to make sure this didn’t happen. It wasn’t an accident. This was allowed so they could start the “we’re all going to die!” narrative. (Sound familiar?) The desired end result is control. Control over content, control over which companies are successful, ….CONTROL. Which govt types demand full control over everything? Communists. Think about that.
We are in the 3rd major industrial revolution. Motors ~ 100 years ago. Internet ~25 years ago. Super Internet ~ now. We can be part of it or we can relinquish control to a few power hungry communists. We decide. We need to vote like we understand the stakes.
if i understand this correctly, at it’s core, AI is indeed automated hacking.
no wonder the developers want to be indemnified.
AI is useful, but those seeking to harness it for personal power and control are not.
so, if liability protections are not granted, and AI is not within the purview of governmental regulation,
can we expect a better product?
AI can only go as rogue as a gun sitting on a table can go rogue.
It’s the operator that was going rogue. No one else and nothing else.
Just noticed that if you replaced in the “NYT AI Meddled” blurb “Open AI Systems” with Russia it still reads the same…
It’s like a Template!