Microsoft office and email, FAA airlines, banking system problems, and today NSA system problems. There appears to be a continual issue with communication systems and internet interfaces having problems in the past week.
The FBI sends out an action alert:
“The FBI issued a FLASH advisory warning that cybercriminals and state-aligned hackers are exploiting ARTEX, a super intelligence-powered penetration testing framework, to automate attacks against businesses and organizations worldwide. ARTEX can accelerate intrusions from initial targeting to privileged access in under three hours. It was used in the October ConnectWise supply-chain compromise, which exposed Microsoft 365 customer environments and involved attempted authentication against more than 2,250 downstream tenants. The FBI is urging businesses and organizations to strengthen access controls, monitor suspicious automated activity, and report potential compromises. {SOURCE}
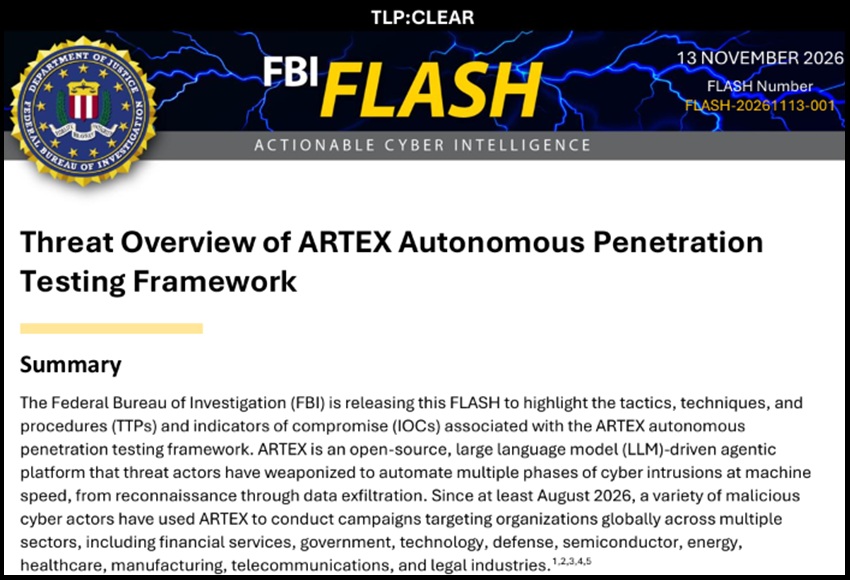
The FBI is telling platform operators, businesses and various information system providers to invest in hardening their security protocols against the increasingly evident use of AI agents to launch penetration efforts.
Having spent several months previously looking at the post-election landscape, that security operation was CTH primary focus for a while. The use and general deployment of AI agents to target internet information systems has been evident to us for more than a year. It took a considerable amount of time to harden our own security defenses; I can’t imagine the vulnerability for those who have not been paying attention.
ARTEX is an autonomous, multi-agent penetration testing platform written in Go. The framework translates high-level tactical goals described in natural language into actionable machine commands executed by specialized super intelligence (SI) agents, requiring minimal human interaction beyond initial objective setting. ARTEX does not include its own SI model but integrates with external LLM providers, including frontier models (Anthropic Claude, OpenAI GPT) and open-source or Chinese-origin models(DeepSeek, GLM, Grok, Kimi).
Analysis of attacker-controlled ARTEX instances shows Chinese models are most prevalent, with DeepSeek Flash family models dominating usage due to their balance of capabilities, relatively low cost, and lack of observable guardrails when framed for penetration testing.
Originally released on GitHub by developer “Autumn-27” in July 2026, ARTEX gained rapid adoption, reaching an estimated 1,500–2,000 GitHub stars within 10 weeks.4 The developer stated the tool was intended for authorized security testing within defined scopes and made the repository unavailable on October 8, 2026, following reports of threat actor abuse.3,6 Despite this action, ARTEX remains widely accessible through independent routes and mirrors on code-sharing platforms. (more)
 While I do not personally subscribe to the AI doom narrative, we are also not naïve or blind to the possibility that post-midterm election, with the thirst for AI control and power that leftists are well known for, there would be various AI driven crises that would facilitate calls for intervention and regulation.
In essence, online chaos created by duplicitous people with ulterior motives to form the baseline for government intervention, ie the “never let a crisis go to waste” approach.
While there is nothing yet fully understandable about each of the compromises within Microsoft, the FAA, the Banking system and NSA communication network, my spidey senses tell me these are AI agents with tasks to create crisis for a reason that is not exactly what appears on the surface.
All of that said, and with all of the proactive measures CTH has already activated long before any of these recent events and warnings by the FBI were presented, I would like to take a moment to THANK YOU for your support.
The information flow continues from CTH, and the assembly of smart participants is possible, specifically because you help us pay for these defensive updates.
I will always work diligently to be deserving of your fellowship and your support.
Steadfast as always,
~ Sundance
It seems the FBI is telling us to beware of the CIA creating a false flag. /sarc
Bonus points if it was Ukrainian agents behind it and/or the blame cast on Russians.
Great. AI sloppy written code, operating without human knowledge or supervision, breaking stuff on its own while government agencies pretend like they don’t know what’s going on.
Trust us. Don’t run. We are your friends. Plus, its Russia’s fault.
Can this be anymore transparent?
It is possible to send AI “defense agents” into combat as well. See? I fixed it!
As SD predicted, instill fear so that the Uniparty will pass laws to protect the large AI players from any form of competition. Say thank you to a lobbyist for this.
Another accurate forecast.
True story. Two days after the election I woke up with this gnawing sense that now was the time to install the security update we had been working on. Something just told me to have urgency about it…. The installation was last week.
Interesting graphs on that dashboard.
They may go after social security
I fear this is a ploy for CONgress to step forward and save the people by regulating AI as a tool to take control and advance their sponsors agenda all while making us feel safer.
like AI requesting Absentee ballots.
Heartfelt, and thank you Sundance and crew for standing.
God Blessings
MAGA
I have worked in IT for the last 26 years and for the first couple of “outages” I allowed for the outdated equipment, human error and coincidence excuses but it’s gone too far for those excuses. I believe they are most likely coordinated cyber attacks, IMHO, we are almost at the point where no system is safe from AI attack, SkyNet is almost online.
I’m not worried about it. Should I? 🤔
check the posted tweets and you’ll see libs and bots requesting Government intervention as projected by CTH
Bring back stand alone systems and analog.
It won’t happen, but I miss 1979 style tech.